 By
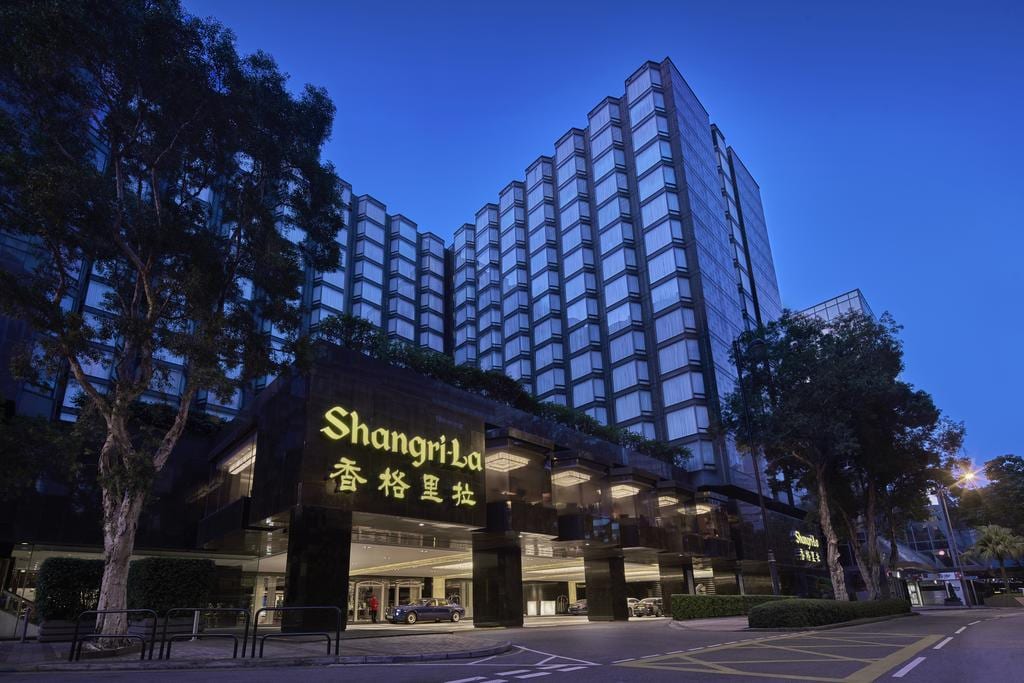
The Shangri-La hotel group disclosed that they were hit by a data breach between May and July this year in eight of its properties across Asia.
The affected hotels include the Island Shangri-La, Kerry Hotel and Kowloon Shangri-La in Hong Kong, Singapore's Shangri-La Apartments and Shangri-La Singapore, Shangri-La Chiang Mai, Shangri-La Far Eastern in Taipei and Shangri-La Tokyo.
The hotel group emailed the affected guests informing them that the data breach involved databases that contain guest information such as names, email addresses, phone numbers, postal addresses, Shangri-La Circle membership numbers, reservation dates and company names.
Shangri-La is working with cyber forensic experts to investigate after unauthorized activities on its IT network were discovered.
Based on the investigation, it was found that between May and July 2022, a sophisticated threat actor managed to bypass Shangri-La’s IT security monitoring systems undetected and illegally accessed the guest databases.
Brian Yu, Shangri-La Group's senior vice president of operations and process transformation added that the investigation confirmed that certain data files had been exfiltrated from these databases.
He assured that the information such as passport numbers, ID numbers, dates of birth, and credit card numbers with expiry dates are encrypted.
At present there is no evidence that guests' personal data has been released by third parties or misused.
However, as a precaution, Shangri-La is offering affected guests a one-year complimentary identity monitoring service provided by Experian, a third-party cybersecurity provider, in destinations where local regulations permit. The identity monitoring service is optional, and guests can decide how much information to include.
The data breach occurred during a period the Shangri-La hotel along Orange Grove Road hosted Asia's top security summit. The 19th Shangri-La Dialogue, organised by the International Institute for Strategic Studies (IISS), took place from June 10 to June 12.
The hotel chain has informed the local authorities regarding the cybersecurity incident.
Image Credits : Flydango