 By
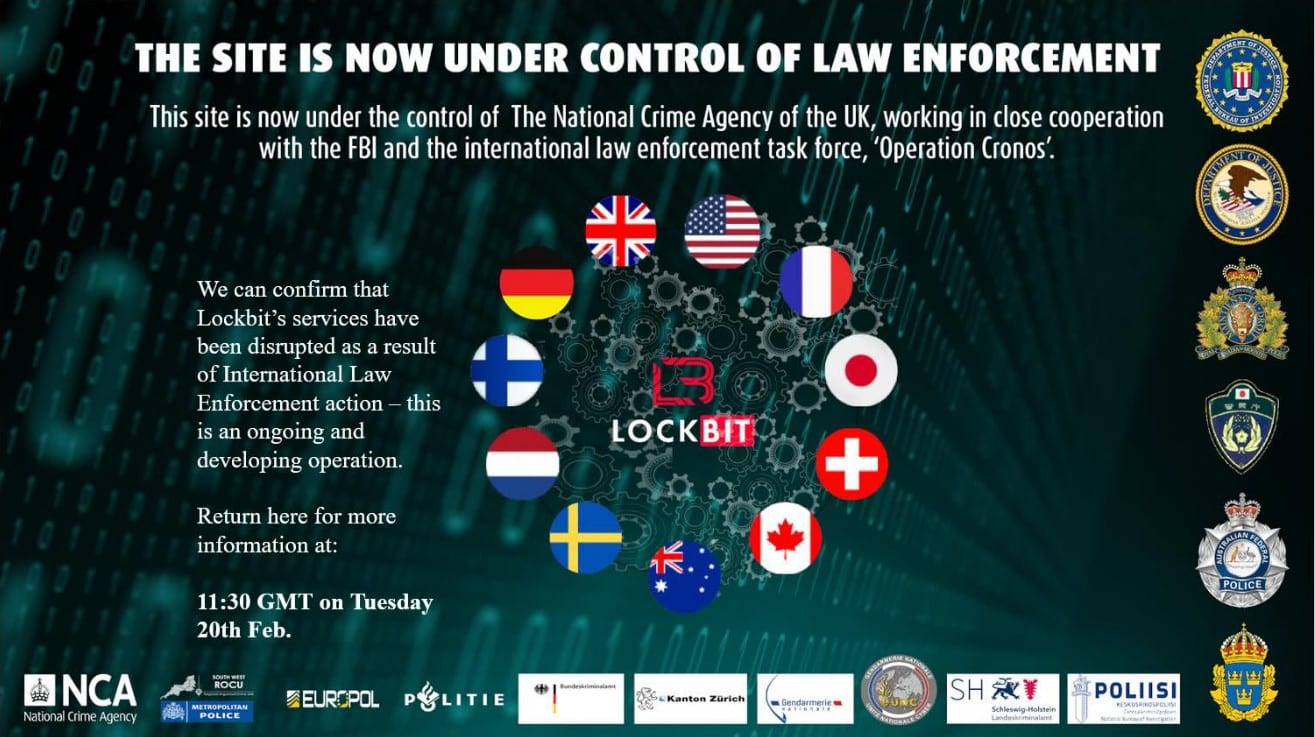
The U.K. National Crime Agency (NCA) confirmed that law enforcement agencies from 10 countries have disrupted the notorious LockBit ransomware operation in a joint operation known as ''Operation Cronos."
It also announced the arrest of two LockBit actors in Poland and Ukraine. Over 200 cryptocurrency accounts linked to the group have been frozen. Indictments and sanctions have also been unsealed in the U.S. against two other Russian nationals who are alleged to have carried out LockBit attacks.
Artur Sungatov and Ivan Gennadievich Kondratiev (aka Bassterlord) have been accused of deploying LockBit against numerous victims throughout the U.S., including businesses nationwide in the manufacturing and other industries, as well as victims around the world in the semiconductor and other industries, per the U.S. Department of Justice (DoJ).
Kondratyev has also been charged with three criminal counts arising from his use of the Sodinokibi, also known as REvil, ransomware variant to encrypt data, exfiltrate victim information, and extort a ransom payment from a corporate victim based in Alameda County, California.
LockBit has been described as the "world's most harmful cybercrime group."
As part of the takedown efforts, the agency said it took control of LockBit's services and infiltrated its entire criminal enterprise. This includes the administration environment used by affiliates and the public-facing leak site hosted on the dark web.
In addition, 34 servers belonging to LockBit affiliates have also been dismantled and more than 1,000 decryption keys have been retrieved from the confiscated LockBit servers.
LockBit ransomware-as-a-service (RaaS) operation surfaced in September 2019 and has since targeted a wide range of high-profile organizations worldwide. It is run by a threat actor known as LockBitSupp.
The attacks follow a tactic called double extortion to steal sensitive data prior to encrypting them, with the threat actors applying pressure on victims to make a payment in order to decrypt their files and prevent their data from being published.
The ransomware group is also infamous for experimenting with new methods for pressuring their victims into paying ransoms.
Triple extortion is one such method which includes the traditional methods of encrypting the victim's data and threatening to leak it, but also incorporates distributed denial-of-service (DDoS) attacks as an additional layer of pressure.
According to Eurojust and DoJ, LockBit attacks are believed to have affected over 2,500 victims all over the world and netted more than $120 million in illicit profits.
A decryption tool has also been made available via No More Ransom to recover files encrypted by the ransomware at no cost.